

Depending on how you look at it, digitization can be both transformative and disruptive, allowing businesses to operate at a speed and scale previously unimaginable. But from a security standpoint, digitization has let the genie out of the bottle and there’s no reversing it.
For the most part, touchpoints used by organizations to interact, communicate, or transact with suppliers, customers, and partners are digital (or fixed on becoming so). This digital transformation makes it much easier to impersonate, manipulate, fake, or steal stuff—and this includes identities, not just data.
THREE COMMON TYPES OF IMPERSONATION ATTACKS
An impersonation attack exploits the trust that a business, brand, or individual has earned for the purposes of compromising an entity. These attacks assume many shapes and sizes. Common impersonations devised by cybercriminals include:
1. EMAIL IMPERSONATION
Email spoofing isn’t anything new; what is noteworthy is the relative speed and sophistication attackers use to carry these out. Threat actors go to extra lengths by creating look-alike domains to ensure their communications appear genuine. Further, they also adopt the writing tone and style of their targets and deliver tailored messages. According to researchers at Darktrace, almost one in two emails now involve some kind of spoofing or impersonation.
2. SOCIAL MEDIA IMPERSONATION
Popular social media platforms such as Facebook, X, and LinkedIn are a breeding ground for scammers and hackers. Their modus operandi is simple: They impersonate well-known brands and individuals by creating seemingly authentic profiles that bear similar names, profile photos, and descriptions.
What’s worse, adversaries harness large language models like ChatGPT to create autonomous bots that are highly persuasive and convincing. In the second quarter of 2023, researchers witnessed a “22% increase in key personnel and corporate social media impersonation accounts.”
3. VOICE AND VIDEO IMPERSONATION
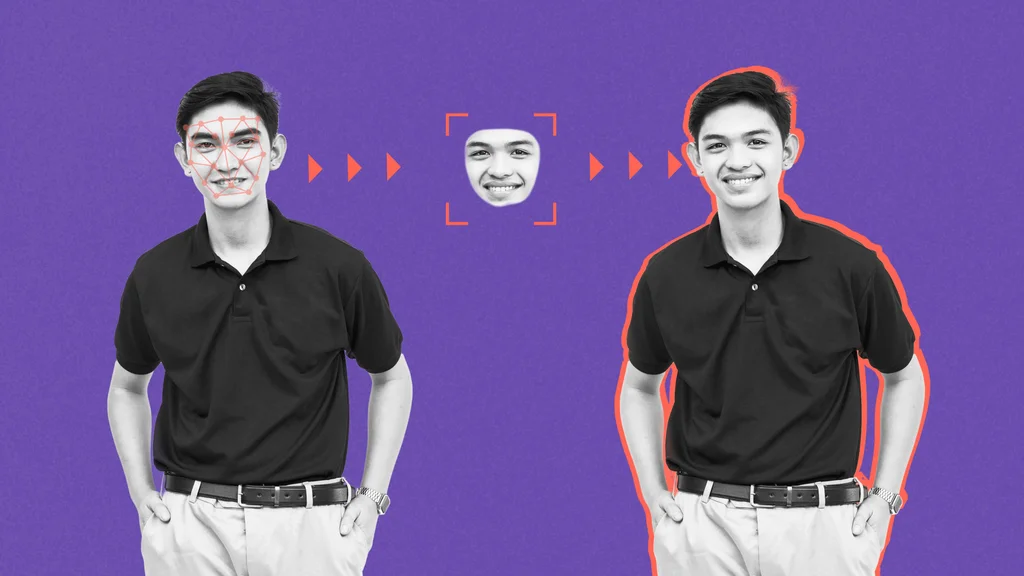
Thanks to recent advances in generative AI, the line between what is real and what is fake has grown blurry. Threat actors can clone voices and generate images and video for the purposes of scamming or phishing; all they need is a three-second audio, a few photos, or a short video clip, which can be easily obtained from public sources or social media. Studies show impersonation attempts using deepfakes jumped by almost 3000% in 2023.
PHISHERS AND IMPERSONATORS CAN ATTACK IN MANY WAYS
Attackers and cybercriminals can leverage impersonation techniques to attack organizations in several ways. For instance:
• They can use impersonation to steal credentials from gullible users. These credentials can then further be used to access intellectual property, conduct reconnaissance, or make lateral movements in the victim’s environment.
• They can leverage impersonation techniques to fool sophisticated biometric authentication (for example, audio and facial recognition) and overcome other cybersecurity defenses like multi-factor authentication.
• Scammers can use AI impersonations to design advanced forms of business email compromise (BEC) or CEO fraud.
• Threat actors, rogue competitors, or nation-state-sponsored cybercriminals can weaponize deepfakes to create and spread disinformation, mistrust, panic, and confusion. This can have a major downstream impact on financials, stock prices, employee morale, market reputation, and relations with partners or customers.
HOW BUSINESSES CAN DEFEND AGAINST IMPERSONATION ATTACKS
Organizations can help mitigate the risk of impersonation attacks by following these best practices:
1. TRAIN EMPLOYEES TO RECOGNIZE AND REPORT IMPERSONATIONS
Since impersonation attacks rely on legitimate channels (such as email, social media, and text) for execution and often contain no malware code, most cybersecurity controls will fail to detect them. The only defense organizations have against impersonation attacks is human intuition.
If organizations leverage phishing simulation platforms (full disclosure: KnowBe4 provides this service), they can train employees to identify attacks and build security intuition. Well-trained employees can instantly recognize deceptive practices and report impersonation attempts.
2. DEPLOY STRONG PASSWORDS, MFA, AND AN INTEGRATED SECURITY SYSTEM
Employees should be trained to use long and complex passwords so that their credentials cannot be easily stolen. Security teams should employ phishing-resistant multi-factor authentication so that even if credentials are stolen, MFA can prevent attacks from escalating. In addition, siloed security tools simply do not cut it anymore. It is important that organizations deploy an integrated security solution such as XDR or SASE so organizations can block lateral movements.
3. PROACTIVELY HUNT DOWN IMPERSONATIONS
If you encounter phishing attacks that involve impersonations, do not take them lightly. Try to identify the root cause behind the attack. Check whether your credentials have appeared in data breaches using sites like haveibeenpwned.com. Use the help of professionals to track down any phishing kits being sold on the dark web that impersonate your brand. Try proactively scanning and tracking social media handles to discover duplicate profiles that are misrepresenting or mimicking the business or key individuals. Share an email address where employees can report instances of impersonations.
The Identity Theft Resource Center predicts organizations will witness record levels of impersonation attacks in 2024. Preventing impersonations is certainly a challenge, but not impossible. By enforcing security policies that enhance security intelligence and intuition, organizations can be successful at mitigating impersonation attacks.
Stu Sjouwerman is the Founder and CEO of KnowBe4 Inc., the world’s largest Security Awareness Training and Simulated Phishing platform.